 Segurança· · 2 min
Ransomware Mayhem Continues.
Today, cybersecurity is in the spotlight with a mix of zero-day vulnerabilities, malware targeting critical infrastructures, and significant funding rounds in the industry. As threats evolve, so do the defenses, with key agencies urging immediate action. It's a crucial moment to stay informed and proactive.
Ransomware Mayhem Continues
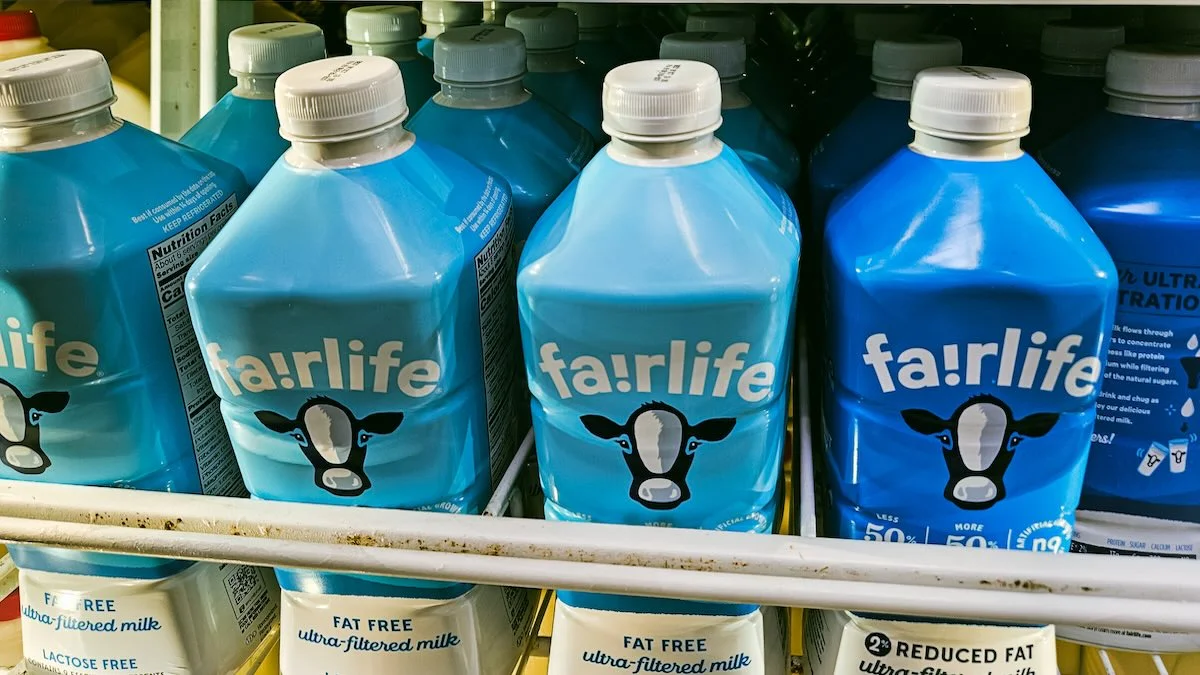
Coca-Cola's Fairlife hit pause on production due to a ransomware attack, joining the ranks of major companies facing disruptions. Nichirei, Japan's frozen food giant, is also grappling with operational impacts following a cyberattack. These incidents highlight the relentless nature of ransomware threats in today's digital landscape.
The Gentlemen ransomware group has taken the lead as the most active cyber extortionist, with 300 attacks reported in just three months. This shift illustrates the growing sophistication and prevalence of ransomware, emphasizing the need for heightened cybersecurity measures.
Zero-Day Vulnerabilities: A Growing Concern
CISA has added a critical SharePoint zero-day vulnerability to its list of actively exploited threats. This flaw, CVE-2026-58644, poses a significant risk as it allows attackers to execute malicious code remotely. Immediate patching is urged for all affected agencies.
Meanwhile, Windows LegacyHive's zero-day exploit grants hackers admin privileges, complicating the security landscape further. The need to address these vulnerabilities rapidly has never been more urgent.
Emerging Threats: New Malware and Botnets

The NadMesh botnet is actively hunting for exposed AI services, aiming to steal cloud keys and Kubernetes tokens. This highlights the evolving tactics of cybercriminals leveraging cloud technology for their schemes.
In another alarming development, seven malicious npm packages have been found using blockchain command-and-control to deliver a RAT. Developers need to be vigilant, as the lines between legitimate and malicious software blur.
Funding and Growth in Cybersecurity
Risk Ledger has secured $32 million in Series B funding, positioning itself as a key player in supply chain security. Their network-first platform aims to combat modern cyber risks effectively.
Beacon Security also raised $13 million to enhance its security data platform, emphasizing the growing need for robust cybersecurity solutions. These investments reflect the industry's positive trajectory amid rising cyber threats.
CISA Urges Immediate Action on Exploited SharePoint Zero-Day
CISA has warned of a critical zero-day vulnerability in SharePoint that is being actively exploited. The flaw allows attackers to execute arbitrary code, prompting federal agencies to patch it immediately.
Coca-Cola Suspends Production Due to Ransomware Attack
Coca-Cola's Fairlife halted production following a ransomware attack that compromised production systems. The company activated incident response protocols and is investigating the incident.
New NadMesh Botnet Targets AI Services
A new botnet, NadMesh, is actively searching for exposed AI services to steal cloud keys and Kubernetes tokens. This highlights the evolving tactics of cybercriminals.
- CISA Mandates Urgent Patch for Fortinet VulnerabilitiesCISA has mandated urgent patches for Fortinet vulnerabilities that are actively exploited. — Infosecurity Magazine
- Ernst & Young Discloses Data BreachErnst & Young reported a data breach due to a compromise of a third-party support system. — BleepingComputer
- Details of Alan Turing’s Voice Encryption SystemA recent auction revealed details of Turing's wartime voice encryption project, Delilah. — Schneier on Security
- Fresh SharePoint Vulnerability Exploited Soon After DisclosureA newly disclosed SharePoint vulnerability is being actively exploited, prompting urgent action. — SecurityWeek
- US Charges Two Over Money LaunderingTwo individuals are charged with laundering $43 million from investment fraud schemes. — BleepingComputer
Esta edição foi útil?
Um clique basta — isso orienta a próxima.