 Ingegneria· · 2 min
AI Models on the Rise.
Today’s tech news is buzzing with AI advancements and critical security updates. From Google's Gemini 3.5 rollout to a worrying npm package compromise, the landscape is shifting fast. Keep an eye on these developments — they might impact your next project.
AI Models on the Rise
Google just dropped Gemini 3.5, promising major enhancements for agentic workflows and coding. This model is built for handling complex tasks and is already available globally. Meanwhile, Cursor's Composer 2.5 is upping the ante with better reliability for long-running tasks and improved communication styles.
In the open-source arena, the hsrs project is making waves by simplifying Rust bindings for Haskell, making cross-language integration smoother than ever. AI is not just evolving — it's redefining how we think about software development.
Security Breaches Rock the Community
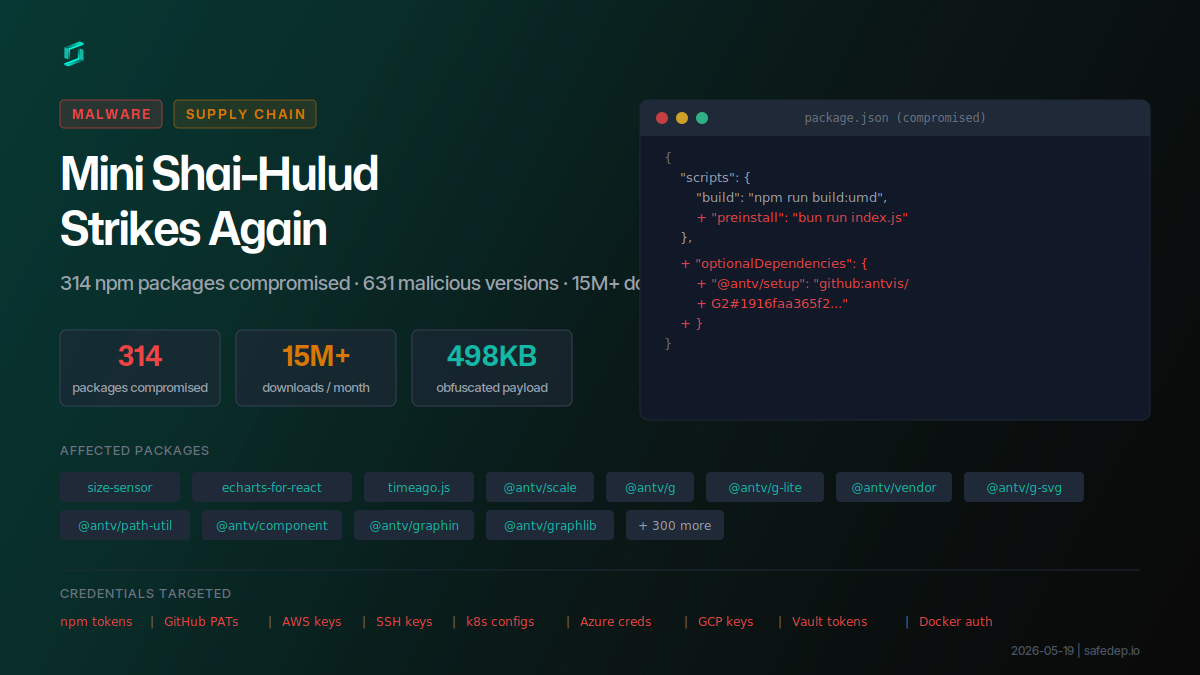
A serious npm compromise saw 317 packages hijacked, potentially affecting millions of developers. The malware used here is sophisticated, harvesting credentials and injecting malicious code into CI/CD pipelines.
On another front, a CISA contractor accidentally leaked sensitive AWS GovCloud keys on GitHub. Experts are calling it one of the most significant government data leaks in recent history. This emphasizes the urgent need for better security practices across the board.
Innovative Tools for Developers
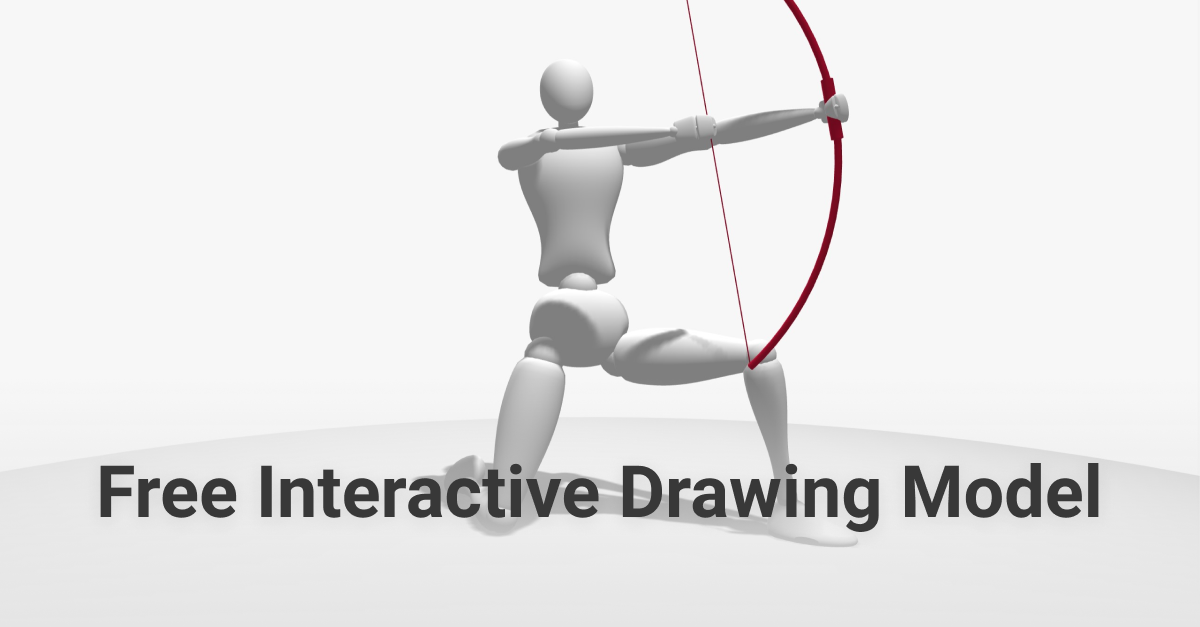
Introducing SetPose, a handy 3D pose maker for artists that simplifies model posing with intuitive controls. This tool could save countless hours in the creative process, making it a must-try for designers.
Meanwhile, the recent OpenBSD 7.9 release brings new features and enhanced security measures. If you’re looking for a stable and secure OS, now’s the time to check it out.
Gemini 3.5: A Significant Leap in AI
Google has introduced Gemini 3.5, designed for complex agentic workflows and coding tasks. This model is now live and aims to enhance user interaction with AI-driven tools.
317 npm Packages Compromised
A single compromised npm account led to a burst of malicious package uploads. This incident highlights the vulnerabilities in open-source ecosystems and the risks developers face.
CISA Admin Leaked AWS GovCloud Keys on GitHub
A contractor for CISA accidentally exposed sensitive AWS credentials on GitHub, raising alarms about government data security. This leak underscores the importance of stringent security measures.
- Google I/O is LiveJoin the livestream of Google I/O for exciting updates and announcements. — Google
- Apple Unveils New Accessibility FeaturesApple introduces features to enhance accessibility powered by Apple Intelligence. — Apple
- Copy Fail, Dirty Frag, and Fragnesia Kernel VulnerabilitiesThe Linux kernel is facing multiple privilege escalation vulnerabilities. — Gentoo
- RabbitMQ vs Kafka: Choosing the Right Messaging SystemA deep dive into the strengths and weaknesses of RabbitMQ and Kafka. — Dev.to
- NestJS vs Express: Which One Should You Choose in 2025?A comparative analysis of NestJS and Express for backend development. — Dev.to
- How the Internet Actually Works: Understanding Client-Server ArchitectureAn insightful guide on client-server architecture with real code examples. — Dev.to
- I’ve Built a Virtual Museum of Operating SystemsExplore a virtual museum showcasing historical operating systems. — Virtual OS Museum
Questa edizione ti è stata utile?
Basta un clic: orienta la prossima.