 Seguridad· · 2 min
Ransomware Strikes Again.
Today's cybersecurity news is buzzing with incidents from ransomware attacks to new AI initiatives. Companies are scrambling to bolster defenses as threats evolve. Data breaches are impacting millions, reminding us that vigilance is key in this digital age.
Ransomware Strikes Again
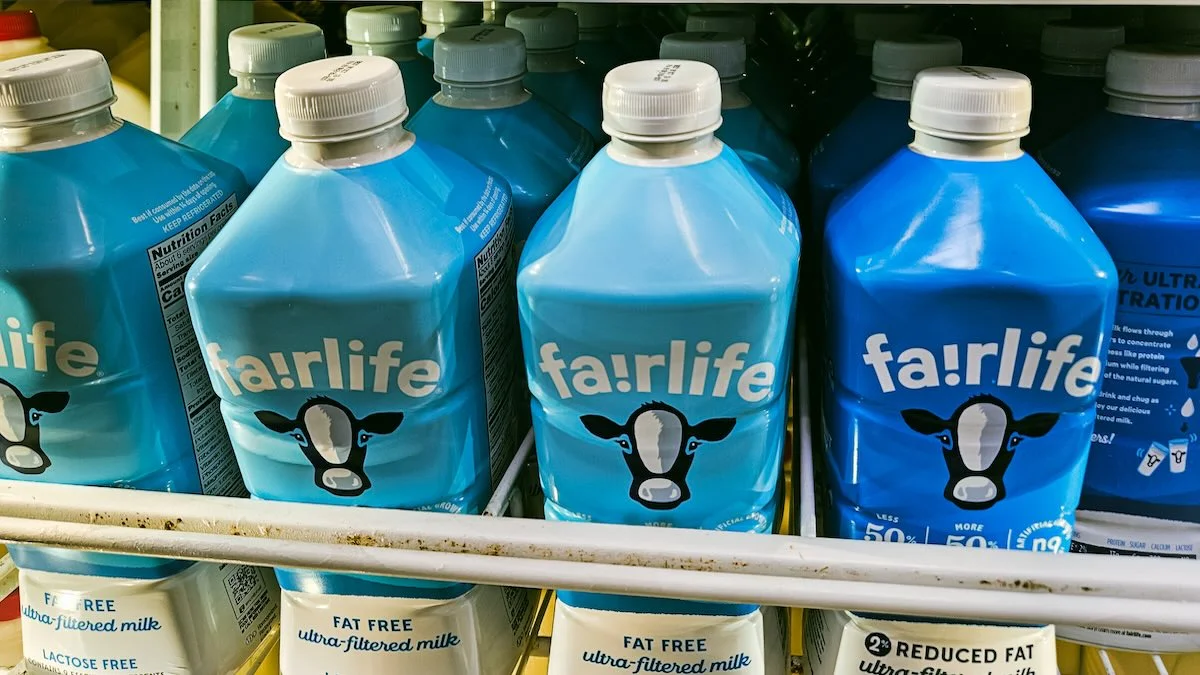
Coca-Cola recently confirmed a data breach following a ransomware attack on its subsidiary, Fairlife. The Anubis group claims to have stolen 1TB of sensitive data, highlighting the increasing audacity of cybercriminals.
In another case, Ernst & Young reported a breach attributed to the ShinyHunters group, which accessed sensitive client tax information. These incidents underscore the urgent need for robust cybersecurity measures across all sectors.
Evolving Threats and New Defenses

The cybersecurity landscape is shifting. GitHub has introduced a three-day cooldown for Dependabot to prevent poisoned package adoption, while PyPI has enacted policies to secure older releases from exploitation.
Meanwhile, new AI models like Anthropic's Opus 5 are enhancing vulnerability detection but still lag in exploit development. As AI becomes more integrated, the race is on to ensure security outpaces threats.
Mobile Security Under Fire
Lookout's Mobile Security Exposure Center (MSEC) reveals serious vulnerabilities hidden within mobile apps. Notably, the WolfSSL flaw can compromise banking apps, urging organizations to gain visibility into application dependencies.
Meanwhile, hacked public Wi-Fi gateways are being exploited to harvest corporate credentials, underscoring the need for secure network practices, especially in public settings.
AI Security Initiatives on the Rise
Tech giants including Nvidia have launched the Open Secure AI Alliance to advance AI safety. This coalition aims to share tools and models designed for securing AI systems, reflecting a collective push for robust cyber defenses as AI adoption increases.
CrowdStrike also joined the initiative, emphasizing the importance of open models in securing AI environments. Collaboration is key as threats become more sophisticated.
Coca-Cola Confirms Data Breach After Fairlife Ransomware Attack
Coca-Cola confirmed a ransomware attack on Fairlife, with data theft claims by the Anubis group. The breach involved 1TB of sensitive data, raising concerns over corporate security protocols.
Ernst & Young Data Breach Claimed by ShinyHunters Extortion Gang
ShinyHunters claimed responsibility for a data breach at Ernst & Young, gaining access through a supply-chain attack. Sensitive client documents were reportedly compromised.
New GitHub, PyPI Policies Boost Supply Chain Security
GitHub and PyPI have rolled out new policies to enhance supply chain security. These measures aim to prevent the adoption of poisoned packages and secure older releases.
- Cognyte Sells a Mobile Cell Surveillance VanCognyte's new surveillance technology simulates mobile phone towers to track nearby devices, raising privacy concerns. — Schneier
- Beelzebub Raises $3.4 Million for Hacker-Trapping PlatformBeelzebub secures funding to enhance its AI-driven platform designed to trap and contain hackers in real-time. — SecurityWeek
- Dysphoria IoT Botnet Adds Blockchain C2 and Victim Relays After JackSkid DisruptionFollowing disruptions, the Dysphoria botnet evolves with new blockchain-based command and control capabilities. — The Hacker News
- SourTrade Malvertising Campaign Secretly Builds Malware in the BrowserSourTrade's new strategy uses browser-based assembly for malware delivery, evading traditional detection methods. — Infosecurity Magazine
- Nvidia and Tech Giants Launch AI Security AllianceNvidia leads a coalition aimed at developing open-source security solutions for AI systems. — SecurityWeek
- Shadow AI Agents Are MultiplyingThe rise of shadow AI agents poses new risks, requiring organizations to maintain visibility and control. — BleepingComputer
¿Te resultó útil esta edición?
Un clic basta: nos ayuda a mejorar la próxima.