 Seguridad· · 2 min
Nation-State Threats Ramp Up.
Cybersecurity is heating up with major vulnerabilities, nation-state threats, and evolving attack strategies. From AI-assisted exploits to data extortion trends, today's landscape is a battleground for digital safety. Stay alert — these developments can impact anyone, from corporations to individuals.
Nation-State Threats Ramp Up
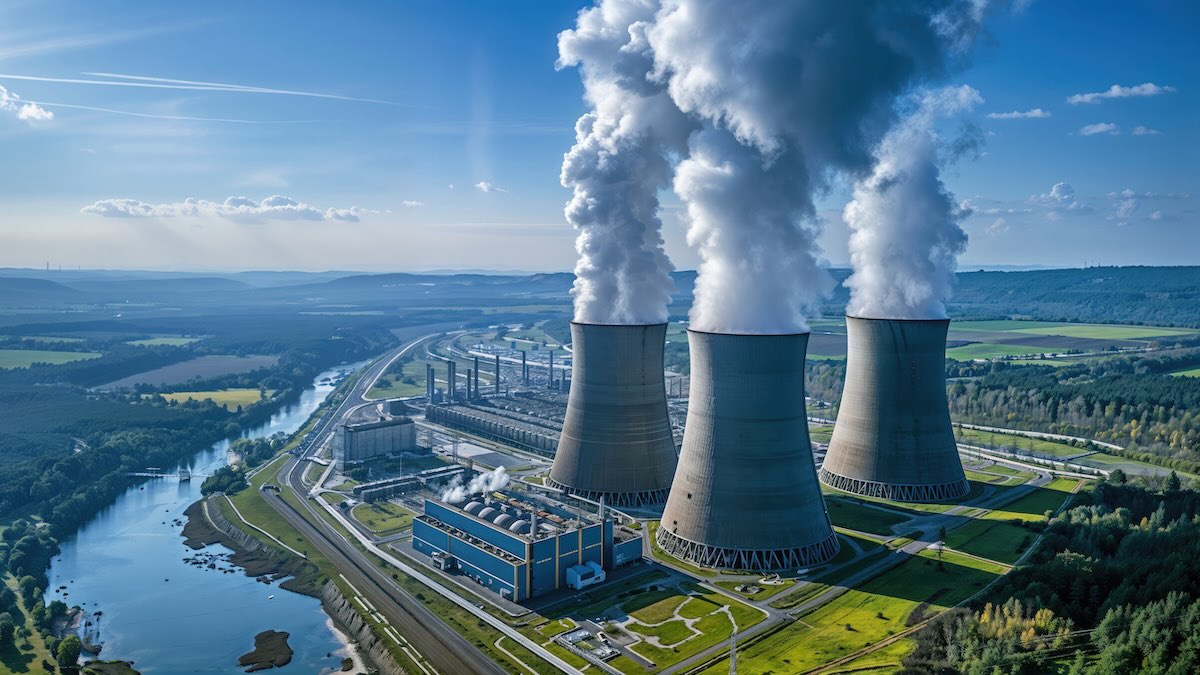
Recent reports highlight a surge in cyber-espionage, particularly from Iranian and Chinese actors targeting national interests. Poland's nuclear research center faced a thwarted attack, believed to be Iranian in origin. Meanwhile, a China-linked group has been infiltrating Southeast Asian militaries, gathering sensitive information for years.
These incidents underscore the escalating stakes in global cyber warfare. As nation-states ramp up their cyber capabilities, organizations must remain vigilant against sophisticated threats that can compromise critical infrastructure.
The Evolution of Cybercrime

Cybercrime is shifting from traditional ransomware to pure data theft for extortion, as seen in Google’s recent findings. The Cl0p group’s campaign against Oracle EBS customers exemplifies this trend, with attackers exploiting zero-day vulnerabilities for financial gain.
Additionally, the FBI is seeking help tracking a malware campaign linked to Steam, highlighting how even gaming platforms are not safe from cyber threats. This evolution poses new challenges for cybersecurity teams, who need to adapt to the changing tactics of cybercriminals.
AI: A Double-Edged Sword

Artificial intelligence is being used by attackers to enhance their strategies, outpacing defensive measures. A new report reveals that threat actors are exploiting AI capabilities to identify vulnerabilities and execute attacks faster than ever before.
Conversely, organizations are racing to integrate AI into their cybersecurity frameworks. This arms race means that both sides need to innovate rapidly, making the cybersecurity landscape more dynamic — and dangerous.
Vulnerabilities on the Rise
New vulnerabilities are being discovered in popular software, with CISA flagging a critical flaw in the Wing FTP Server that is actively exploited. This flaw allows attackers to execute remote code, posing significant risks for users.
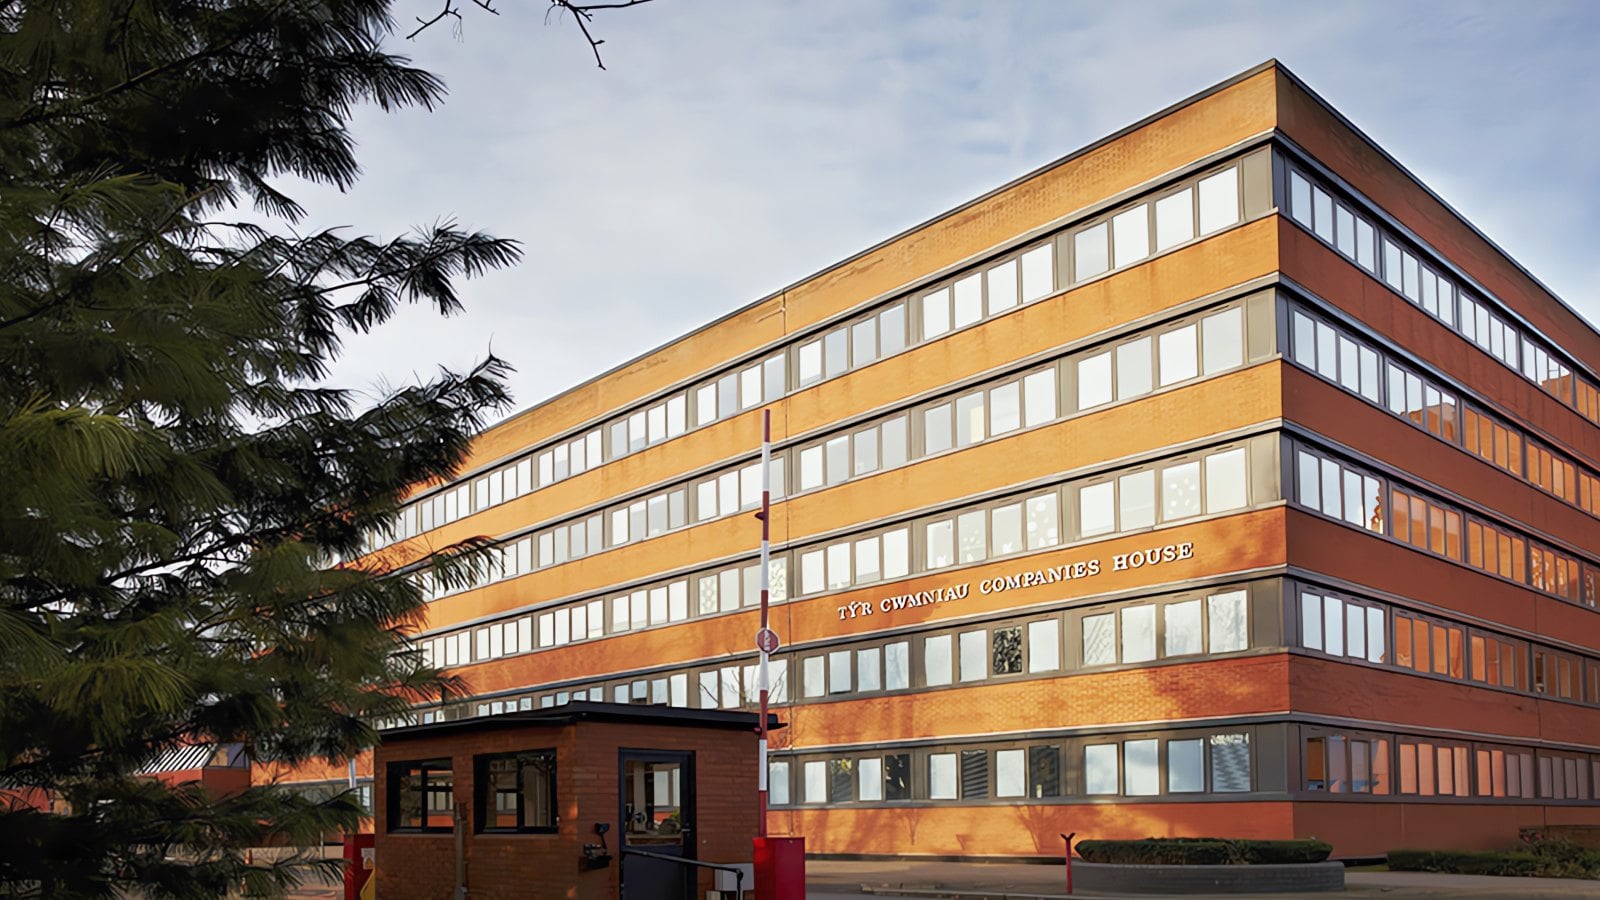
Meanwhile, the UK’s Companies House confirmed a security flaw that exposed sensitive business data for months. These incidents highlight the urgent need for swift patching and proactive security measures to safeguard against exploitation.
The number of Linux systems potentially affected by newly discovered vulnerabilities in AppArmor.
FuenteThe number of fake shipment tracking campaigns detected monthly, a sign of rising online scams.
FuentePercentage of ransomware intrusions that involve data theft for extortion, according to Google Threat Intelligence.
FuenteIranian Cyber Threat Evolution: From MBR Wipers to Identity Weaponization
Iranian cyber actors are shifting tactics from disruptive malware to identity abuse, integrating cyber operations into their strategy. This evolution raises the stakes for global organizations facing increased risks.
FBI Calls for Help to Track Steam Malware Campaign
The FBI is seeking assistance from gamers who may have downloaded malware via Steam, highlighting ongoing cyber threats in the gaming world. The campaign targets users to gather sensitive information.
- Android 17 Blocks Non-Accessibility Apps from Accessibility APIAndroid 17 updates aim to prevent malware abuse via the Accessibility API, enhancing user security. — The Hacker News
- Stryker Attack Wiped Tens of Thousands of DevicesA cyberattack on Stryker led to the remote wiping of devices, highlighting vulnerabilities in corporate IT environments. — Bleeping Computer
- CISA Flags Wing FTP Server FlawCISA warns of an actively exploited flaw in Wing FTP Server, urging immediate action from users. — Bleeping Computer
- ClickFix Campaigns Spread MacSync macOS InfostealerFake AI tool installers are being used to spread a new macOS infostealer called MacSync. — The Hacker News
- Shadow AI is EverywhereOrganizations must manage the risks associated with widespread use of AI tools and ensure security governance. — Bleeping Computer
¿Te resultó útil esta edición?
Un clic basta: nos ayuda a mejorar la próxima.