 Security· · 2 min
Patch Tuesday: A Busy Month for Microsoft.
Today in cybersecurity, major players are stepping up their defenses against rising threats. From Microsoft patching critical zero-days to the fallout from an Iranian hack on MedTech giant Stryker, it's a busy day for security updates. Plus, new funding rounds signal that innovation in threat detection is on the rise.
Patch Tuesday: A Busy Month for Microsoft

Microsoft has patched 84 vulnerabilities this month, including two zero-days that had been publicly disclosed. This includes an SQL Server privilege escalation flaw, which, if exploited, could let attackers gain significant control. Sysadmins are urged to act quickly to mitigate these risks.
This month’s Patch Tuesday also highlights the increasing importance of proactive security measures as cyber threats evolve. With organizations relying heavily on cloud services, the urgency for timely updates has never been greater.
Stryker Takes a Hit from Iranian Hackers
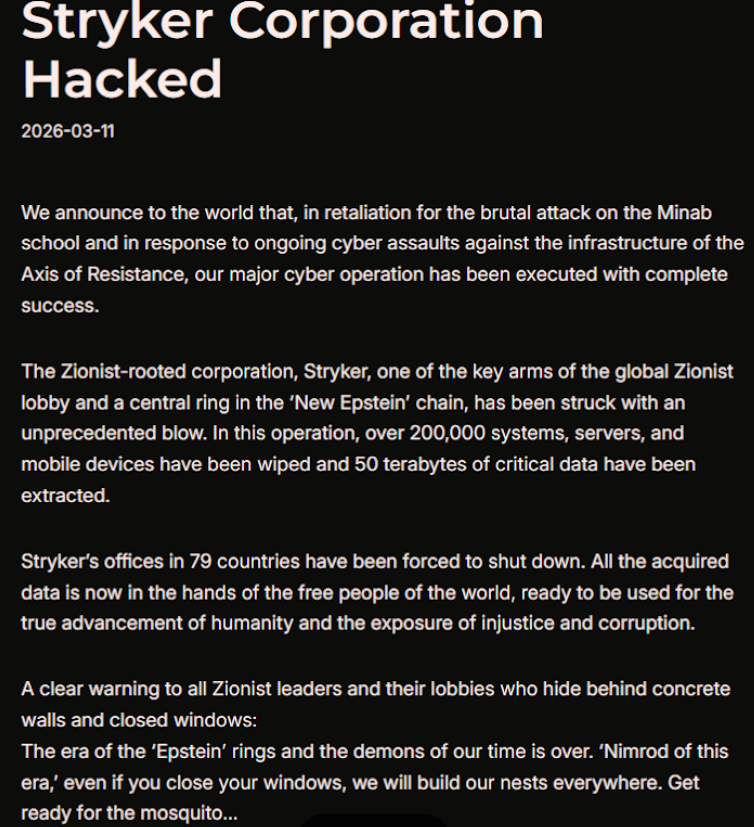
Medical tech firm Stryker was hit hard by a wiper malware attack claimed by the Iranian-linked Handala group. The attack reportedly wiped over 200,000 systems, crippling operations in 79 countries and compromising 50 terabytes of data. This incident emphasizes the serious risks that critical infrastructure faces from nation-state actors.
As tensions rise globally, companies in sensitive sectors must ramp up their defenses against targeted cyber threats. The Stryker breach is a stark reminder that even well-protected entities are vulnerable.
Emerging Threats: PhantomRaven & BlackSanta Malware
The PhantomRaven campaign is back with 88 malicious npm packages aimed at stealing developer data. This highlights the ongoing risk in supply chain attacks, especially in open-source environments where trust is paramount.
In another alarming development, BlackSanta malware is disabling security protections before executing its payload. Such tactics make it easier for attackers to harvest credentials and exfiltrate sensitive information, showcasing the sophistication of modern cyber threats.
Funding Fuels Cybersecurity Innovations
Quantro Security has emerged with $2.5 million in funding to enhance its AI-driven cybersecurity solutions. The startup aims to optimize vulnerability management by integrating data from various sources, a crucial step in today's threat landscape.
Additionally, Scanner has raised $22 million to develop an AI-powered threat hunting platform. These investments signal a strong market demand for innovative security solutions that can adapt to evolving cyber threats.
CISA's Urgent Advisories
CISA has ordered federal agencies to patch a critical n8n vulnerability exploited in ongoing attacks. This highlights the need for immediate action as the agency works to bolster defenses across government systems.
With cyber incidents increasing, agencies must prioritize cybersecurity hygiene and stay updated on vulnerabilities to protect sensitive data effectively.
Stryker Hit by Wiper Attack from Iranian Hackers
Stryker has been crippled by a wiper malware attack claimed by an Iranian hacktivist group. Over 200,000 devices were wiped, and critical operations were disrupted worldwide.
PhantomRaven NPM Attack Wave Targets Devs
New PhantomRaven attacks leverage 88 malicious npm packages to exfiltrate sensitive developer data. This ongoing threat emphasizes the need for vigilance in the open-source community.
Microsoft Patches 84 Vulnerabilities, Two Zero-Days
Microsoft's March Patch Tuesday addresses 84 vulnerabilities, including critical zero-days, urging organizations to update their systems promptly.
- Canada Needs Nationalized, Public AICanada is investing in a Sovereign AI Compute Strategy but faces questions about its impact on public interests. — Schneier
- Meta Disables 150K Accounts Linked to Scam CentersMeta cracks down on 150,000 accounts tied to Southeast Asia scam centers as part of a broader anti-scam initiative. — The Hacker News
- CISA Orders Feds to Patch n8n RCE FlawCISA has mandated federal agencies to patch a critical n8n vulnerability that’s being actively exploited. — BleepingComputer
- Wiz Joins Google Cloud as Landmark Acquisition ClosesWiz's acquisition by Google Cloud aims to enhance cloud security capabilities significantly. — SecurityWeek
- Senate Confirms Joshua Rudd to Lead NSAThe Senate confirms Joshua Rudd to head the NSA and Cyber Command, filling a crucial national security role. — SecurityWeek
Was this issue useful?
One click is enough — it shapes the next one.