 安全· · 3 分钟
A Crackdown on Cybercrime: Project Compass.
Today's cybersecurity landscape is buzzing with significant developments, from the arrest of notorious cybercriminals to alarming vulnerabilities affecting both consumer products and enterprise infrastructure. As attacks become increasingly sophisticated, the stakes are higher than ever, highlighting the urgent need for robust security measures. With incidents like the Gardyn smart gardens hack and the exposure of sensitive data through compromised APIs, organizations and individuals alike must remain vigilant amidst a rising tide of threats.
A Crackdown on Cybercrime: Project Compass

A yearlong operation led by Europol, dubbed 'Project Compass', has culminated in the arrest of 30 members of 'The Com', a notorious cybercriminal group linked to significant ransomware attacks and exploitation. This collective, often comprised of young individuals, has engaged in a variety of cybercrimes, including phishing and SIM swapping. The operation highlights the collaborative efforts of international law enforcement to dismantle organized cybercrime syndicates that prey on vulnerable populations and engage in violent extortion tactics.
Project Compass is not just about arrests; it's a wake-up call for the cybersecurity community about the evolving nature of threats. With tactics that span social media and gaming platforms, 'The Com' represents a new breed of criminal organization that leverages technology to manipulate and exploit. The implications of these arrests go beyond immediate security; they signify a concerted effort to address the root causes of cybercrime and protect potential victims.
Rising Vulnerabilities: A Call for Urgent Action
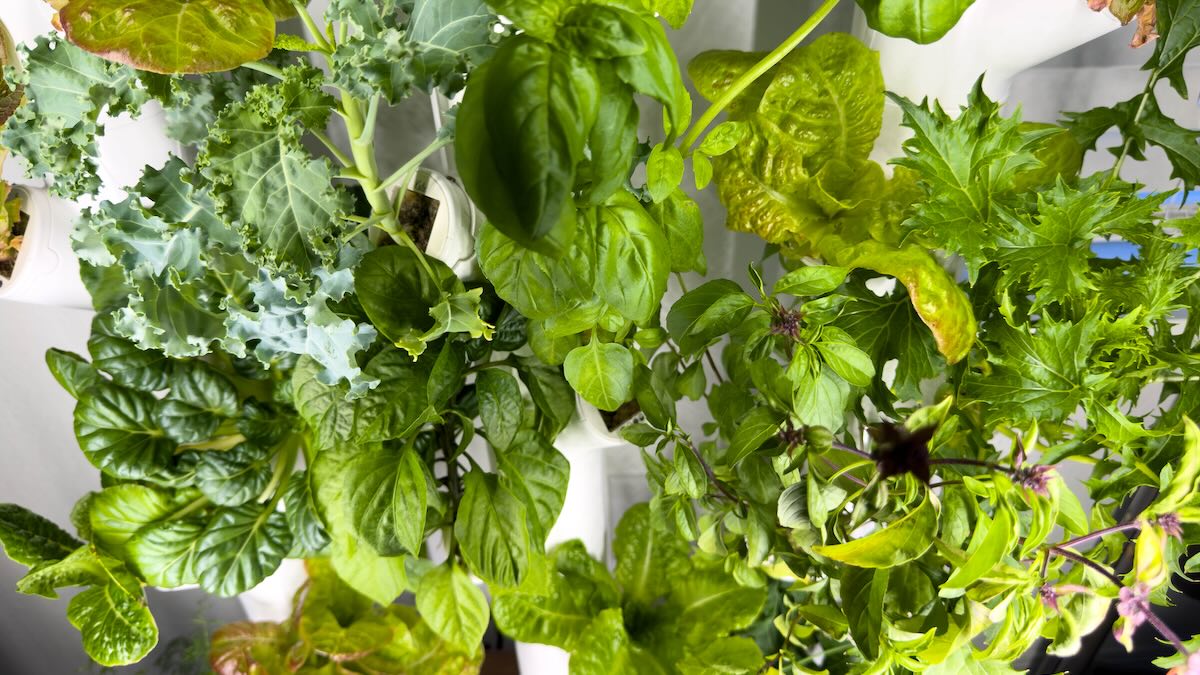
Recent reports expose critical vulnerabilities in widely used technology, such as Juniper Networks' PTX routers and Gardyn's smart garden systems. The Juniper flaw, which allows unauthenticated attackers to execute arbitrary code as root, underscores a significant risk for enterprises reliant on these routers for network integrity. Similarly, Gardyn's smart gardens were found to have multiple vulnerabilities, including hardcoded credentials that could lead to unauthorized access. The potential for exploitation in both cases is alarming, given the increasing reliance on connected devices for everyday tasks.
These incidents serve as a reminder that as our dependence on technology grows, so too does the need for rigorous security measures. Organizations must prioritize patch management and vulnerability assessments to mitigate the risks associated with outdated or improperly secured systems. The onus is on both manufacturers and consumers to advocate for and implement stronger security practices.
The Dark Side of AI: Scams and Exploits
The intersection of AI and cybersecurity has taken a troubling turn, with reports of AI-powered scams gaining traction. A Ukrainian man recently pleaded guilty to running a website that generated fake IDs using artificial intelligence, facilitating a range of fraudulent activities. This highlights the dual nature of AI technology, which can be used for both innovative solutions and malicious purposes. As cybercriminals become more adept at leveraging AI, the potential for harm grows exponentially.
Furthermore, phishing attacks have evolved, with North Korean hackers posing as recruiters to target job seekers in the tech industry. This new tactic not only exploits individuals' ambitions but also underscores the need for increased awareness and education around cybersecurity. As AI continues to develop, establishing ethical guidelines and security protocols will be essential in curbing its misuse.
Approximately 38 million people may have been affected by the recent ManoMano data breach, highlighting the extensive impact of cyber incidents.
来源The UK government claims to have reduced unresolved security flaws by 75% through a new vulnerability monitoring service, showcasing effective government intervention in cybersecurity.
来源Around 900 Sangoma FreePBX instances were found to be infected with web shells, illustrating the ongoing threat of command injection vulnerabilities.
来源Critical Vulnerabilities in Juniper Networks Routers
Juniper Networks has alerted users to a serious vulnerability in its PTX routers that could allow unauthenticated attackers to execute arbitrary code. The implications are severe, as an attacker gaining control could manipulate data flows and breach adjacent networks. The urgency of patching this vulnerability cannot be overstated, especially given the critical role these routers play in enterprise network architecture.
Project Compass: A Major Crackdown on Cybercrime
Europol's Project Compass has successfully dismantled a significant cybercrime network, arresting 30 members of 'The Com'. This operation underscores the growing collaboration between international law enforcement agencies to combat cyber threats. As these groups increasingly target vulnerable populations, this crackdown serves as a crucial step in protecting individuals from exploitation.
Gardyn Smart Gardens Exposed to Remote Hacking
Critical vulnerabilities in Gardyn's smart gardens could have enabled significant security breaches, allowing attackers to execute arbitrary commands and gain complete control of the devices. This situation highlights the need for stringent security measures in IoT devices, especially as they become more prevalent in households. Prompt action and awareness are essential to prevent such threats.
- Trojanized Gaming Tools Spread Java-Based RAT via Browser and Chat PlatformsA new report details how trojanized gaming tools are being used to spread a Java-based Remote Access Trojan (RAT) through popular communication platforms. — The Hacker News
- Meta Files Lawsuits Against Advertisers Over Celeb-Bait ScamsMeta has initiated lawsuits against advertisers in Brazil, China, and Vietnam for running scams that exploit celebrity endorsements. — The Hacker News
- DoJ Seizes $61 Million in Tether Linked to Crypto ScamsThe U.S. Department of Justice has seized $61 million in Tether linked to crypto scams known as 'pig butchering'. — The Hacker News
- Malicious Go Crypto Module Steals Passwords, Deploys BackdoorA malicious Go module has been discovered that steals passwords and deploys a backdoor, raising concerns over supply chain security. — The Hacker News
- APT37 Hackers Use New Malware to Breach Air-Gapped NetworksNorth Korean hackers from APT37 are using new malware to breach air-gapped networks, enhancing their espionage capabilities. — Bleeping Computer
本期内容对你有帮助吗?
点一下就好,这将影响下一期。