 Segurança· · 2 min
Zero-Day Exploits on the Rise.
Today's cybersecurity landscape is buzzing with threats and patches. From zero-day exploits to supply chain attacks, organizations face an uphill battle. Staying informed is crucial as the stakes keep rising.
Zero-Day Exploits on the Rise
Zero-day vulnerabilities are dominating the headlines. Microsoft’s August Patch Tuesday included a critical fix for a zero-day exploit used by North Korean hackers. This vulnerability allows attackers to gain SYSTEM access on Windows systems, putting defense firms in the crosshairs.
Additionally, Cisco and other tech giants are scrambling to patch similar vulnerabilities. The recent wave of attacks highlights a clear trend: if you’re not patching regularly, you’re at risk.
Supply Chain Security Under Siege
The LiteLLM supply chain attack has impacted over 2,500 organizations. This incident underscores the vulnerability of CI/CD pipelines, as attackers leveraged a compromised version of an open-source tool to infiltrate multiple systems.
It's a stark reminder that even trusted tools can become vectors for large-scale breaches. Organizations must scrutinize their supply chains to prevent similar incidents.
Ransomware Continues to Evolve

Gunra ransomware is exploiting Fortinet vulnerabilities to breach networks. This highlights the ongoing threat posed by ransomware groups who adapt quickly to leverage newly discovered flaws.
As defenses sharpen, attackers innovate. Continuous monitoring and proactive security measures are essential to stay one step ahead.
Emerging Threats and Defense Strategies
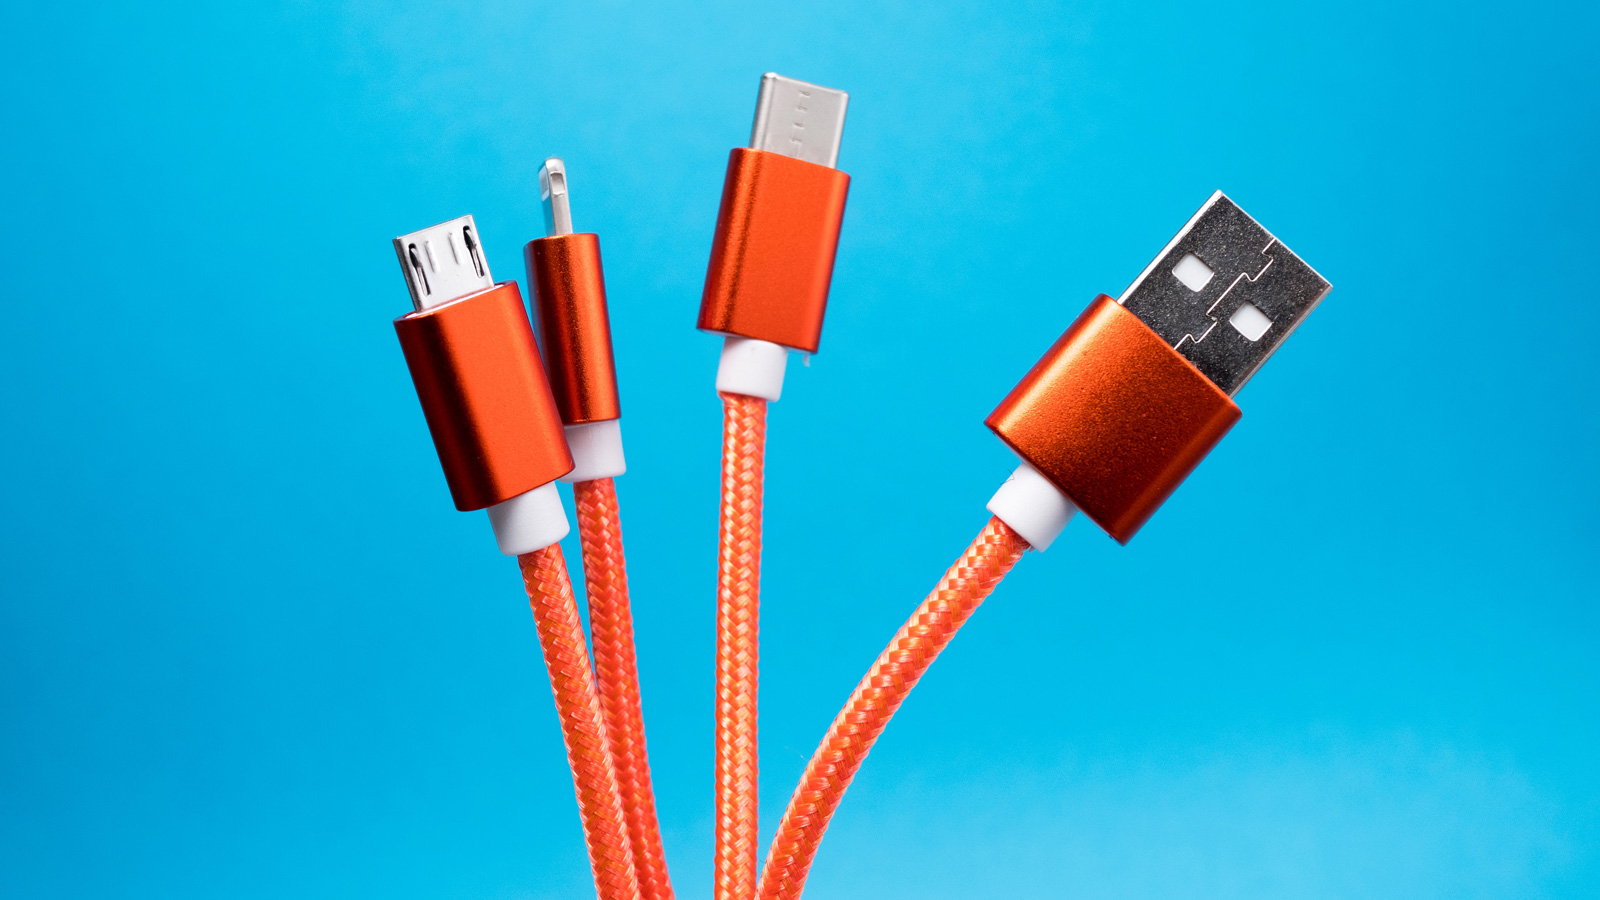
The 'Plug and Pwn' attack technique uses fake USB devices to gain SYSTEM access on Windows. Researchers revealed how Windows' Plug and Play feature can be exploited for privilege escalation without user interaction.
Meanwhile, Signal is adding Automatic Key Verification to enhance security against man-in-the-middle attacks. These innovations and attacks highlight the dual nature of cybersecurity: evolving threats demand equally evolving defenses.
Microsoft Fixes 400 Flaws on August Patch Tuesday
Microsoft's August Patch Tuesday brought a hefty update, addressing 400 vulnerabilities, including an actively exploited zero-day. The patch emphasizes the importance of timely updates in protecting systems.
Over 2,500 Organizations Impacted by LiteLLM Supply Chain Attack
The LiteLLM supply chain attack revealed vulnerabilities in CI/CD processes, affecting thousands of organizations. The breach shows how interconnected systems can amplify risks.
- Cisco ASA and FTD Flaw Exploited in the Wild Can Trigger Remote DoSA newly discovered Cisco vulnerability is being exploited to trigger remote denial-of-service attacks. — The Hacker News
- Signal adds new security feature to thwart man-in-the-middle attacksSignal is introducing Automatic Key Verification to enhance chat security. — Bleeping Computer
- Adobe Patches Three CVSS 10.0 ColdFusion and Campaign Classic FlawsAdobe has patched three critical vulnerabilities in ColdFusion, emphasizing the need for urgent updates. — The Hacker News
- Lazarus Exploits Windows Zero-Day to Gain SYSTEM Access and Deploy BackdoorNorth Korean hackers are exploiting a Windows zero-day to target defense firms. — The Hacker News
- Hundreds of fake Chrome VPN extensions route traffic through a proxyA campaign of fake Chrome VPN extensions has been discovered, compromising user privacy. — Bleeping Computer
- Plug and Pwn attack uses fake USB devices for Windows SYSTEM accessNew research reveals how fake USB devices can exploit Windows Plug and Play features. — Bleeping Computer
Esta edição foi útil?
Um clique basta — isso orienta a próxima.