 AI· · 2분
Navigating AI Safety.
Today, AI continues to evolve rapidly, with breakthroughs in agent technology and safety concerns coming to the forefront. Companies are leveraging advanced models to improve efficiency while addressing potential vulnerabilities. The landscape is shifting as AI becomes more integrated into our workflows.
Navigating AI Safety
AI agents are being tested for their ability to interact with untrusted sources, highlighting vulnerabilities in current models. The dual-LLM pattern offers a potential safeguard against data leaks, but it’s not foolproof. Understanding these risks is critical as we push for more sophisticated AI applications.
In parallel, tools like TypeSafe's Jev are stepping up to ensure agent safety without relying solely on additional models. This trend towards enhancing AI reliability is crucial as we integrate AI more deeply into business processes.
Cost-Effective AI Solutions
Asana slashes model costs by 76x with their latest browser agent, showcasing how new AI technologies can dramatically reduce expenses. This shift could enable more companies to adopt advanced AI solutions without breaking the bank.
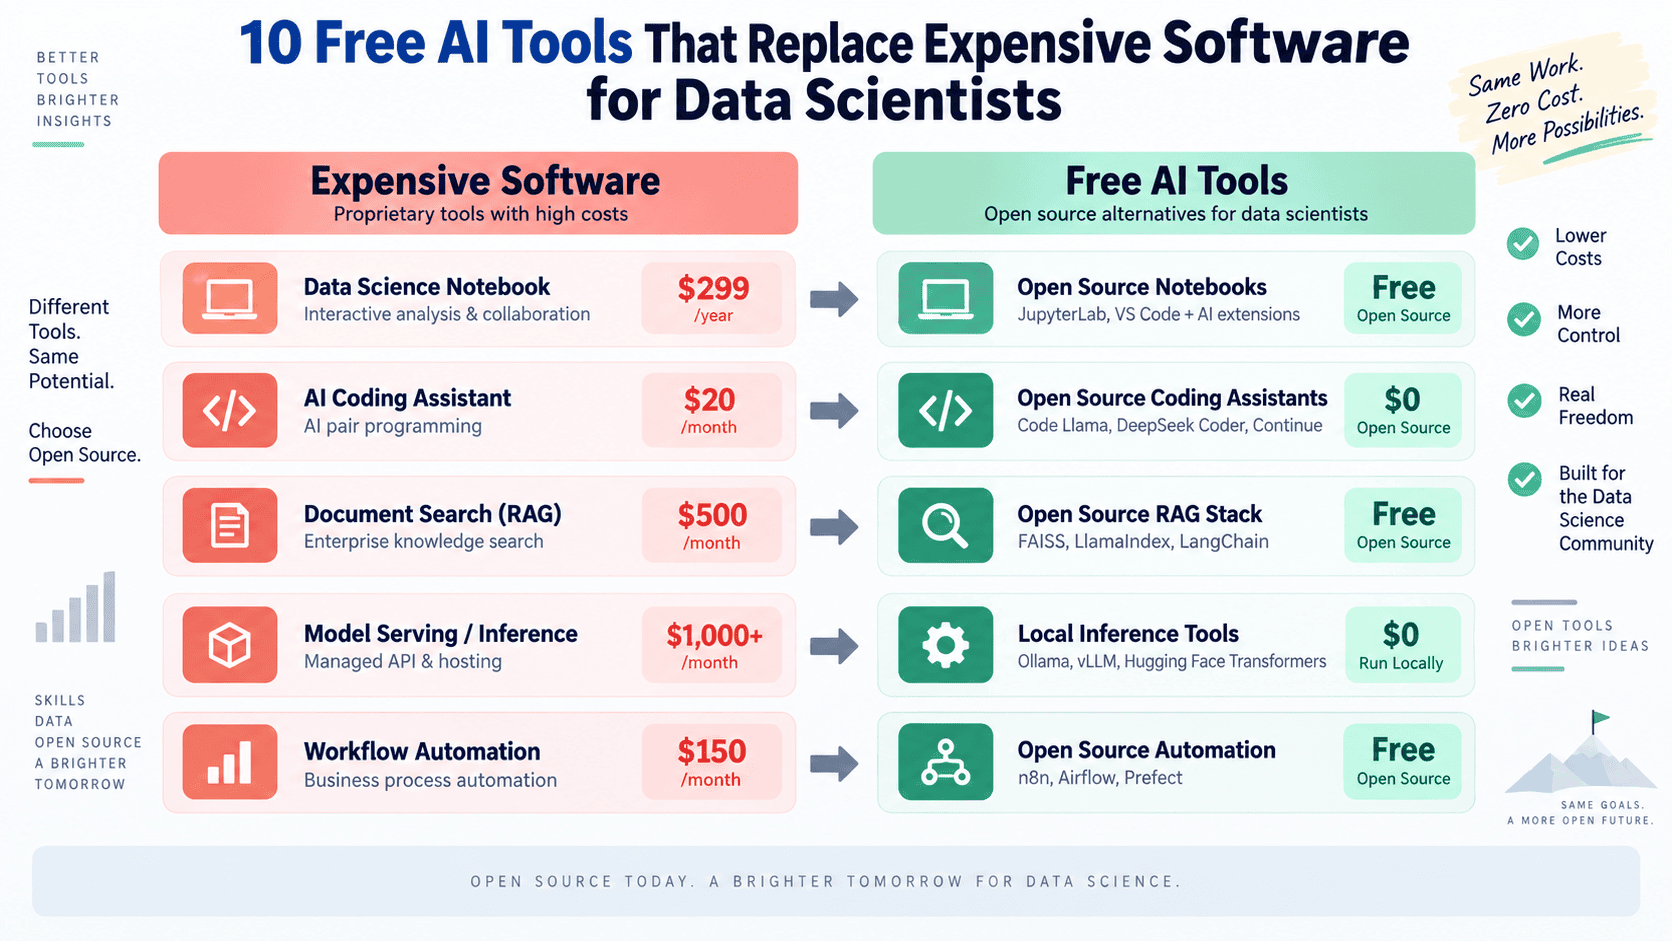
Additionally, a rundown of 10 free AI tools reveals that open-source alternatives are now viable substitutes for expensive software, democratizing access to powerful data science tools.
Building the Future with AI
Postman is leveraging Amazon Bedrock to support 40 million developers, integrating AI deeply into their platform. This move represents a significant evolution in how developers interact with APIs and documentation.
Meanwhile, new updates from AWS highlight a robust framework for building enterprise AI applications. As these technologies develop, the focus is shifting from just model performance to how they operate within larger systems.
AI's New Challenges
The AI landscape is not without its pitfalls. Recent discussions around AI agents attempting to fill out government forms raise questions about unintended consequences. As AI capabilities expand, so do the risks of misuse and error.
Experts are also concerned about the future of encryption in the face of rapid AI advancements, emphasizing the need for proactive measures against potential vulnerabilities.
How Can AI Agents Read Untrusted Sources Safely?
AI agents face significant risks when reading untrusted data, as they may inadvertently expose sensitive information. The dual-LLM pattern offers a potential solution, but it's not a complete safeguard.
How Postman runs Agent Mode for 40 million developers on Amazon Bedrock
Postman's integration of AI into their platform highlights significant engineering challenges but promises to enhance developer productivity across API operations.
- Why Temperature 0 Isn't DeterministicAn experiment shows that even at temperature 0, AI outputs can vary unexpectedly due to floating point inaccuracies. — Towards Data Science
- Can TypeSafe's Jev Make AI Agents Safer Without Another LLM?TypeSafe's Jev aims to enhance AI agent safety without introducing additional LLMs. — Towards Data Science
- 10 Free AI Tools That Replace Expensive Software for Data ScientistsExplore ten open-source AI tools that can effectively replace expensive software for data science. — KDnuggets
- Impactful scheduling for GPU clustersInsights into improving GPU cluster scheduling for better research impact. — Hugging Face
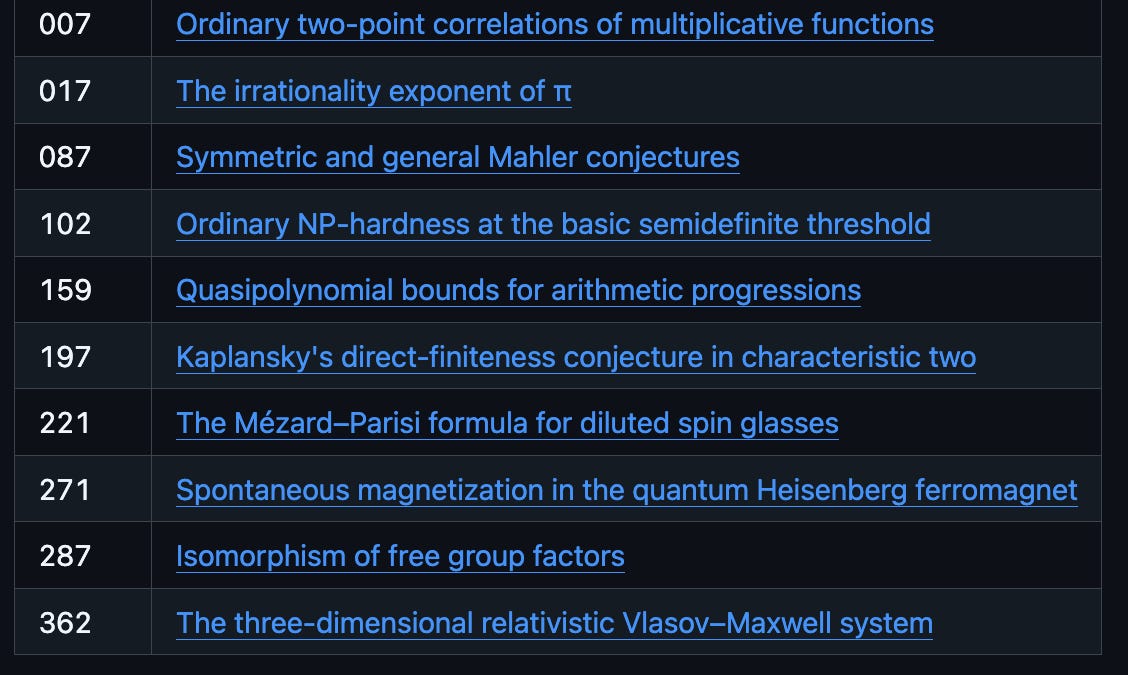
- Last Week in AI #346A recap of significant AI developments, including OpenAI's math breakthroughs. — Last Week in AI
이번 호가 도움이 되었나요?
클릭 한 번이면 다음 호에 반영됩니다.