 Open Source· · 2 min
Godot's Rise Amidst European Independence.
Today, open source is front and center as Europe turns to Godot while AI in enterprise sees costs plummet. Linux security faces challenges, and new tools like GoLand EAP promise exciting features ahead. It's a transformative time in tech, and the ripple effects are palpable.
Godot's Rise Amidst European Independence
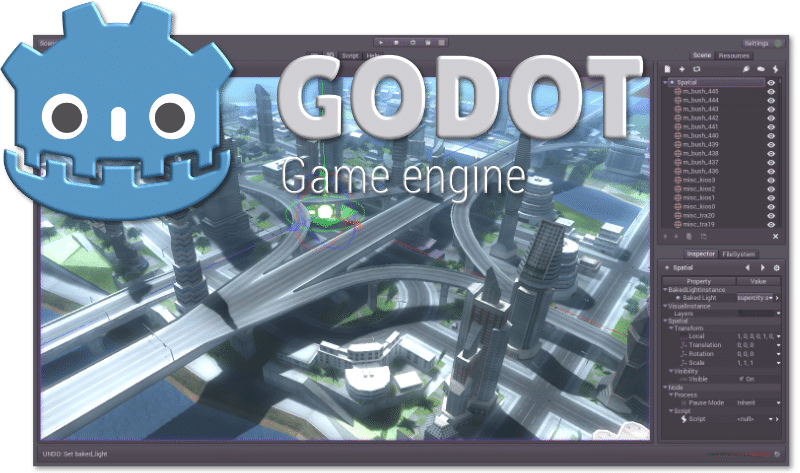
Godot is gaining traction in Europe as developers seek alternatives to US-dominated game engines like Unreal and Unity. With the debate around AI integration and technology sovereignty heating up, Godot's open-source model offers a refreshing solution that sidesteps vendor lock-in.
Critics argue that Godot still lacks certain features, but its flexibility and community-driven updates are winning over many. The recent backlash against Unity's pricing practices has only amplified interest in Godot, making it a serious contender in the game development landscape.
Linux Security Under Pressure
The recent Dirty Frag vulnerability disclosure has stirred controversy within the Linux community. Public code visibility has led to premature disclosures, challenging the traditional embargo practices.
This incident highlights the tension between open-source transparency and the need for coordinated vulnerability disclosure. As developers navigate this complex landscape, the consequences for security practices could be significant.
AI Models Driving Down Enterprise Costs
Open-source AI models are creating a seismic shift in enterprise costs, dropping by 67% over the past year. As multi-model architectures gain traction, companies are ditching single-provider dependencies and embracing flexibility.
With open-source models capturing 38% of enterprise token volume, the landscape is evolving fast. This trend isn’t just about savings; it’s about empowering businesses to innovate without the financial burden.
New Tools on the Horizon
The Early Access Programs for GoLand and ReSharper are now live, offering developers a sneak peek into upcoming features. This is a chance to influence the final product while getting hands-on experience with the latest integrations.
From performance insights to AI enhancements, these tools aim to streamline workflows for developers. Don't miss out on the opportunity to shape the future of your IDE.
SEBI Flags Open Source Supply Chain Risks After Anthropic AI Finds 2000 Vulnerabilities
SEBI has raised alarms about open source software vulnerabilities after Anthropic AI uncovered over 2,000 security flaws in just seven weeks. This report has prompted calls for enhanced cybersecurity measures across India's financial sector.
Public Linux Code Commits Trigger Early Dirty Frag Disclosure
The Dirty Frag vulnerability was disclosed earlier than expected due to public Linux code commits, highlighting the challenges of transparency in open-source security. This incident raises questions about the viability of traditional embargo practices in the open-source space.
- Linux Foundation Backs Open Drivers To Improve Linux Hardware CompatibilityThe Linux Foundation is pushing for open-source drivers to enhance hardware compatibility and reduce reliance on proprietary solutions. — Open Source for You
- The GoLand 2026.2 Early Access Program Has StartedGoLand's EAP is now live, offering developers a chance to test new features and influence the product's future. — JetBrains
- High-Severity Security Issue Affecting TeamCity On-PremisesA high-severity security vulnerability has been identified in TeamCity On-Premises, urging users to update immediately. — JetBrains
- Visual Studio Code 1.120The latest release of Visual Studio Code introduces new features and enhancements for a better coding experience. — Visual Studio Code
- Rider 2026.2 Early Access Program Begins With Performance ImprovementsRider's EAP has launched, focusing on performance improvements and user feedback for the upcoming release. — JetBrains
Questa edizione ti è stata utile?
Basta un clic: orienta la prossima.