 Open Source· · 2 min
Open Source on the Rise.
Today's tech landscape is buzzing with open-source initiatives and security threats. From quantum computing advancements to AI developments, the focus is on collaboration and innovation. Meanwhile, cybersecurity concerns escalate as open-source vulnerabilities rise.
Open Source on the Rise
Open-source projects are gaining momentum with significant contributions. Y Combinator’s QM for AI-agent workflows and Google's Credentio library for content provenance are just a couple of examples. These tools offer flexibility and customization, allowing developers to tailor solutions to their needs.
The open-source quantum computing scene is heating up too. SDT’s partnership with Open Quantum Design is bridging hardware manufacturing with open-source development, making quantum tech more accessible. This collaboration highlights the power of community-driven innovation.
Cybersecurity Concerns
Cyber threats are escalating, with India among the top five APT targets. Kaspersky reports a staggering 37% rise in malicious open-source packages, underscoring vulnerabilities in trusted software. This highlights the urgent need for robust security measures as dependency on open-source components grows.
Moreover, attacks on popular projects like Axios and Notepad++ serve as a wake-up call for developers. Securing the software supply chain is more critical than ever, especially as threats evolve.
AI & Automation in Development
AI is transforming development workflows. Arduino’s new AI coding agent in App Lab allows for interactive development, making coding more intuitive and efficient. This feature enables developers to focus on creativity rather than repetitive tasks, reshaping how projects are built.
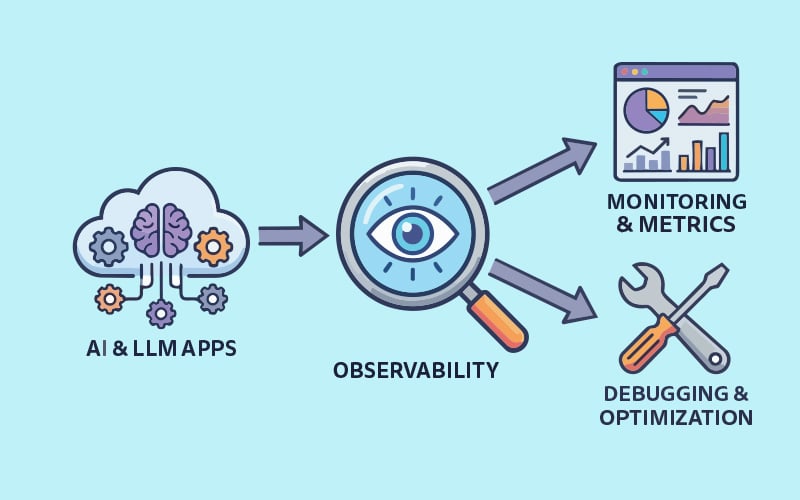
Meanwhile, observability in AI applications is becoming crucial. As AI systems evolve, understanding their behavior in production is key to ensuring reliability and quality. This shift emphasizes the need for tools that provide insight into AI operations.
Fedora Testing & Updates

Fedora 45 is gearing up for major changes, with test days focused on significant updates like OpenSSL 4.0 and RPM 6.1. Community involvement is vital to ensure these updates function across various hardware setups.
As the Linux community rallies to test these changes, it showcases the collaborative spirit that drives innovation in open-source operating systems.
India Among Top Five APT Targets, Open Source Threats Rise 37%
Kaspersky reports a 37% increase in malicious open-source packages, highlighting vulnerabilities in trusted projects. With India listed as a top target, the urgency for enhanced cybersecurity measures is evident.
Y Combinator Open Sources QM For AI-Agent Workflows
Y Combinator’s QM platform enhances AI-agent operations for startups. This open-source initiative allows for tailored workflows, making it easier for teams to coordinate their AI efforts.
Google Open-Sources C++ Library for Content Provenance
Google's Credentio library aids developers in validating content credentials locally. This move emphasizes performance and privacy, essential for media applications handling sensitive data.
- Russell Coker: Hacked by ChinafansRussell Coker shares his experience of a hack on his personal blog, highlighting the importance of vigilance. — etbe
- AMD Video Drivers, LLMs, and Debian KernelsCoker discusses issues with AMD GPUs and the usefulness of ChatGPT for troubleshooting. — etbe
- FrOSCon 2026: TLS TalkSven Hoexter shares insights from his TLS basics talk at FrOSCon 2026. — sven.stormbind.net
- SDT Joins Open-Source Quantum Push With OQDSDT announces its support for open-source quantum hardware development. — Open Source For You
- Test Days for Fedora 45: Help Us Test the Big ChangesFedora 45 is looking for community testers for significant updates. — Fedora Magazine
- Visual Studio Code 1.134 (Insiders)The latest features and updates in the Insiders build of Visual Studio Code. — Visual Studio Code
- Exploring Compose HTML for Server Side RenderingJetBrains explores server-side rendering with Kotlin's Compose HTML. — JetBrains
¿Te resultó útil esta edición?
Un clic basta: nos ayuda a mejorar la próxima.