 Engineering· · 2 min
Security Vulnerabilities in Focus.
Today's tech buzz is all about security, efficiency, and innovation. From critical vulnerabilities in popular libraries to groundbreaking AI advancements, the landscape is shifting rapidly. Buckle up, because there's a lot to unpack.
Security Vulnerabilities in Focus
Node.js just disclosed a serious vulnerability affecting many libraries and applications using Brotli compression (CVE-2026-111497). This flaw could let attackers leak memory or run arbitrary code, impacting a wide range of HTTP services.
Meanwhile, the serialize-javascript package has a Cross-Site Scripting vulnerability (CVE-2026-115897) due to a flaw in its escapeFunctionBody method. Developers are advised to upgrade to version 7.1.3 to mitigate these risks.
AI Breakthroughs

Dessa has launched a groundbreaking conversation model trained solely on speech. This AI can hold natural conversations, capturing emotional nuances like a human.
In another leap, Google’s Data Agent Kit is now generally available, allowing developers to connect coding agents to Google Data Cloud services effectively. It's free and open-source, making it accessible for all developers.
Efficiency Wins
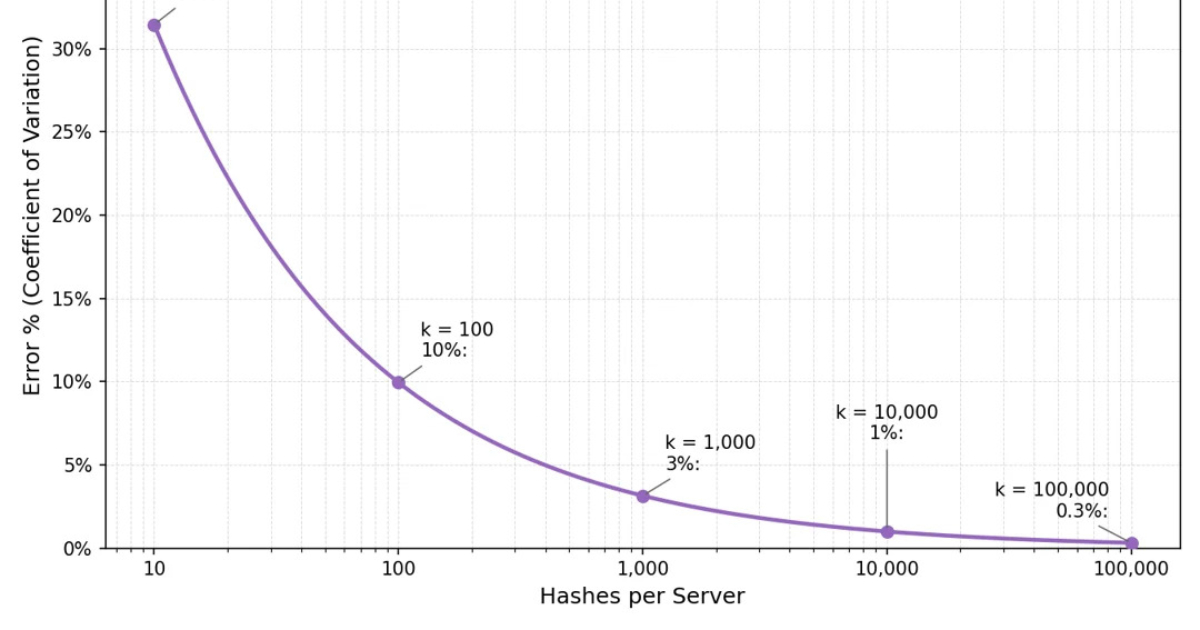
Cloudflare has optimized its consistent hashing algorithm, reclaiming over 100 TB of RAM. This efficiency boost enhances load balancing while reducing memory usage, a win for performance and sustainability.
On the development side, a new guide outlines how to track SaaS signups effectively, ensuring founders know where their users are coming from. It’s a must-read for anyone in the SaaS space.
Shifts in Development Practices

The transition from GitHub to GitLab by Roku developers highlights a growing trend in the industry towards more flexible development environments. This move aims to enhance collaboration among developers.
Additionally, a new tool called PauseDock has emerged, designed to help developers manage unfinished tasks. This local model lets you take breaks without losing your place, fostering better productivity.
Node2Shell Evolves to HTTP2Shell Amid Vulnerability Alerts
Node.js disclosed a significant vulnerability (CVE-2026-111497) affecting many libraries and apps using Brotli compression. This issue highlights the importance of security patches across coding environments.
Dessa's Speech Model Sets New Standards for AI Conversations
Dessa introduces an AI model trained solely on speech, enabling lifelike conversations. This innovation could reshape how we interact with voice AIs.
- How to Find Out Where Your SaaS Signups Come FromA practical guide for SaaS founders on tracking user origins effectively. — Dev.to
- Your 'Pay Now' Button Can Charge TwiceAn insightful look at how idempotency keys can prevent double charges in payment systems. — Dev.to
- PauseDock: Let a Local Model Keep Your PlaceA new tool to help developers manage unfinished tasks and improve productivity. — Dev.to
- Apple Security Research Device Program Now OpenApple's new program facilitates iOS security research with specially designed devices. — Apple
- How Block Blast Harvests Its Players for Ad MoneyAn in-depth analysis of the ad monetization strategies in the game Block Blast. — Ayoships
Was this issue useful?
One click is enough — it shapes the next one.