 Sicherheit· · 2 Min.
Data Breaches on the Rise.
Today’s cybersecurity landscape is filled with high-stakes incidents and alarming trends. From massive data breaches affecting universities and companies to new vulnerabilities that threaten enterprise security, the stakes have never been higher. Keeping your defenses sharp is crucial as attackers evolve their tactics.
Data Breaches on the Rise
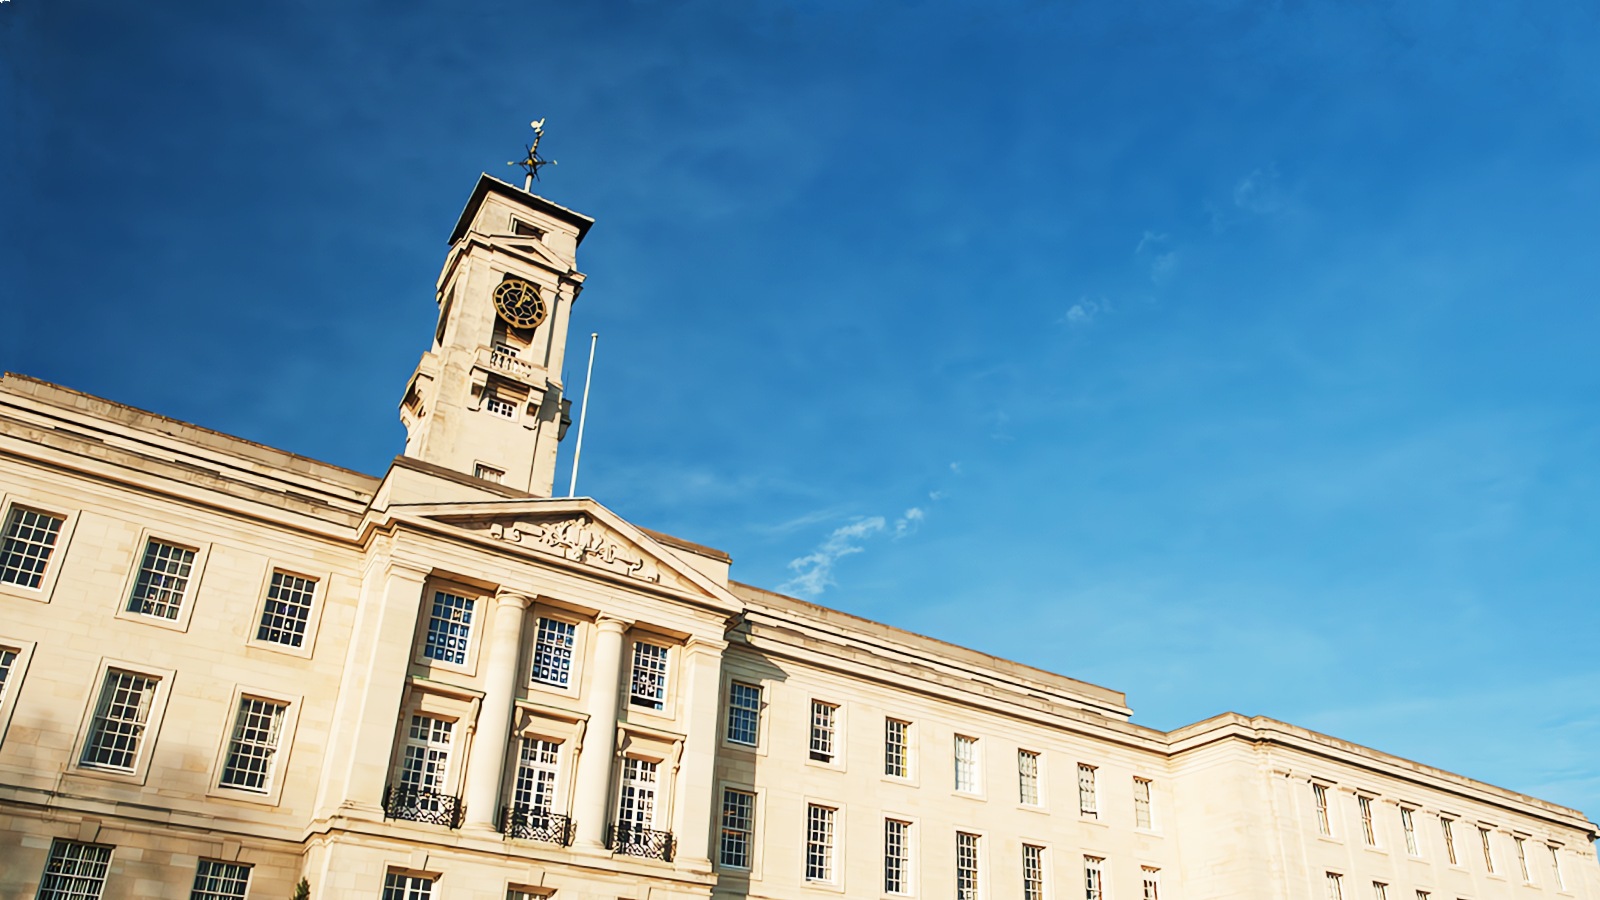
The University of Nottingham has confirmed a significant data breach affecting over 450,000 students. This incident highlights the ongoing risk universities face from cybercriminals, particularly those like the ShinyHunters group that target educational institutions.
In another major case, Coupang, a South Korean e-commerce giant, received a record $409 million fine for a data breach impacting 37 million customers. As regulatory scrutiny tightens globally, companies must prioritize data protection or face severe penalties.
Emerging Vulnerabilities

Microsoft has patched a critical vulnerability in Exchange Server that was actively exploited before the fix. With zero-day attacks becoming more frequent, timely patch management is essential for organizations.
Meanwhile, a new exploit named GreatXML allows attackers to bypass BitLocker protections, showcasing the ever-evolving nature of security threats. Organizations need to remain vigilant against such vulnerabilities.
AI and Cybersecurity
AI continues to be a double-edged sword in cybersecurity. While it can bolster defenses, it's also being weaponized by attackers. New 'agentjacking' attacks can trick AI coding agents into executing malicious commands, emphasizing the need for robust security measures.
Moreover, AI-driven threats are exposing the limits of traditional managed security services. As attackers leverage AI for rapid exploitation, companies must adapt their strategies to keep pace.
Regulatory Pressure Mounts
The U.S. CISA has mandated federal agencies patch critical vulnerabilities within three days, underscoring the urgency of cybersecurity measures in government operations. This directive aims to enhance national security by addressing high-risk flaws quickly.
In the UK, tech giants like Apple and Google face pressure to implement device-level protections against inappropriate content for children. Compliance with such regulations is becoming increasingly essential for tech companies.
Nottingham University Data Breach Exposed
The University of Nottingham confirmed a breach impacting over 450,000 students, attributed to the ShinyHunters group. The incident highlights vulnerabilities in student data management systems and the risks of cybercriminal targeting.
Coupang Fined $409 Million for Data Breach
Coupang has been fined a record $409 million for a massive data breach affecting 37 million customers. This case sets a precedent for stringent enforcement of data protection regulations in South Korea.
- Microsoft Fixes BitLocker Recovery BugMicrosoft has resolved a BitLocker recovery issue affecting Windows Server 2025. — Bleeping Computer
- GitHub to Disable npm Install Scripts by DefaultGitHub is disabling npm install scripts by default to prevent supply chain attacks. — The Hacker News
- Ivanti Sentry Vulnerability ExploitedA critical vulnerability in Ivanti Sentry is being actively exploited by attackers. — Bleeping Computer
- FBI Seizes Websites Used by China to Recruit US WorkersThe FBI has taken down websites that were part of a Chinese recruitment operation targeting US citizens. — SecurityWeek
- Oracle Addresses PeopleSoft VulnerabilityOracle has issued a security alert for a PeopleSoft vulnerability amid reports of exploitation. — SecurityWeek
War diese Ausgabe hilfreich?
Ein Klick genügt – er prägt die nächste Ausgabe.