 Sicherheit· · 2 Min.
New Malware Tactics on the Rise.
Today in cybersecurity, we’re seeing a mix of fresh threats and significant crackdowns. From North Korea's latest malware tactics to critical vulnerabilities being exploited, it's a busy day in the digital battleground. The constant cat-and-mouse game between attackers and defenders shows no signs of slowing down.
New Malware Tactics on the Rise

North Korea's APT37 is now leveraging Facebook for social engineering to deliver RokRAT malware. This tactic highlights how attackers are evolving their methods to exploit popular platforms for malicious purposes.
Meanwhile, the JanelaRAT malware is targeting financial institutions in Latin America, successfully executing thousands of attacks. The shift towards specialized malware in specific regions underlines the need for tailored defense strategies.
Big Moves Against Phishing and Fraud
Operation Atlantic has taken down a major phishing network responsible for over $20 million in fraud. This international effort saw over 20,000 victims identified, showcasing the scale of crypto-related scams.
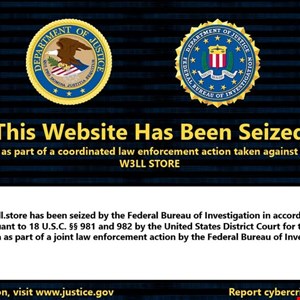
In another significant blow to cybercrime, the FBI and Indonesian authorities dismantled the W3LL phishing operation, seizing its infrastructure and arresting its developer. These actions highlight the ongoing commitment to combating online fraud.
Critical Vulnerabilities Demand Attention
Adobe has rolled out an emergency fix for a zero-day flaw affecting Acrobat and Reader, which has been actively exploited. Users are urged to update immediately to avoid potential breaches.
CISA has also added seven new known exploited vulnerabilities to its catalog, emphasizing the importance of timely patching and awareness in organizations. Cybersecurity isn't just reactive; it's about staying ahead.
Operation Atlantic Seizes $12m in Crypto Losses
Law enforcement agencies from the UK, US, and Canada have identified over 20,000 victims of approval phishing schemes, freezing $12 million in stolen assets. This operation underscores the global scale of cryptocurrency fraud.
FBI Dismantles $20m Phishing Operation W3LL
The FBI and Indonesian authorities have taken down the W3LL phishing network responsible for over $20 million in fraud. This operation highlights the collaboration between international authorities to tackle cybercrime.
- OpenAI Revokes macOS App Certificate After Malicious Axios Supply Chain IncidentOpenAI is rotating its macOS code-signing certificates after a supply chain attack involving Axios. — The Hacker News
- Fake Claude Website Distributes PlugX RATA fraudulent site posing as Anthropic's Claude app was found distributing remote access trojans. — SecurityWeek
- Gmail Brings End-to-End Encryption to Android and iOS for Enterprise UsersGoogle has launched end-to-end encryption for Gmail on mobile devices, enhancing security for enterprise users. — SecurityWeek
- Mirax Android Trojan Turns Devices Into Residential Proxy NodesThe new Mirax Trojan is turning Android devices into proxy nodes, significantly broadening its impact. — Infosecurity Magazine
- CISA Adds Seven Known Exploited Vulnerabilities to CatalogCISA has added several newly exploited vulnerabilities to its catalog, urging quick remediation. — CISA
War diese Ausgabe hilfreich?
Ein Klick genügt – er prägt die nächste Ausgabe.